Documentation DigaSystem
2026.2.0 2025.2.0 2023.2.0
2026.2.0 2025.2.0 2023.2.0

Configure DPE web application to use OIDC via AD FS

To enable the new logon mechanism you have to change your web.config in the following way:

(1) disable forms auth by commenting it out:

<!--
    <authentication mode="Forms">
      <forms name="MyFormsAuthCookie" timeout="1440" slidingExpiration="true" loginUrl="Logon.aspx" ticketCompatibilityMode="Framework40"/>
    </authentication>
-->


(2) enable AD FS OIDC support by specifying an AdFsServer:

Given that you have the following AD FS configuration...
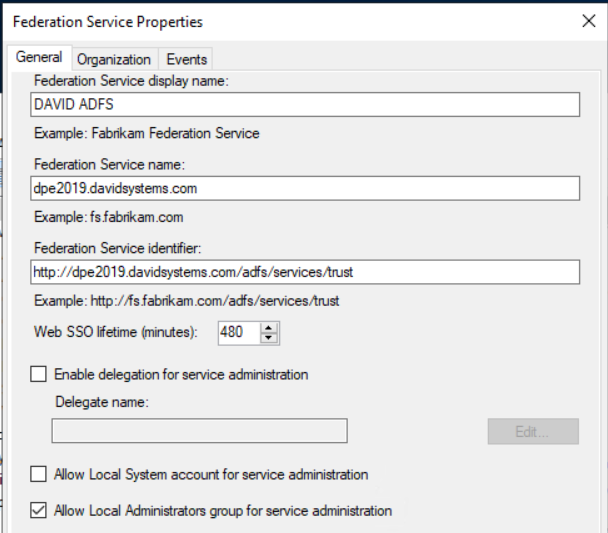
FederationServices_Properties.png

and the following AD FS Application Group for DPE...
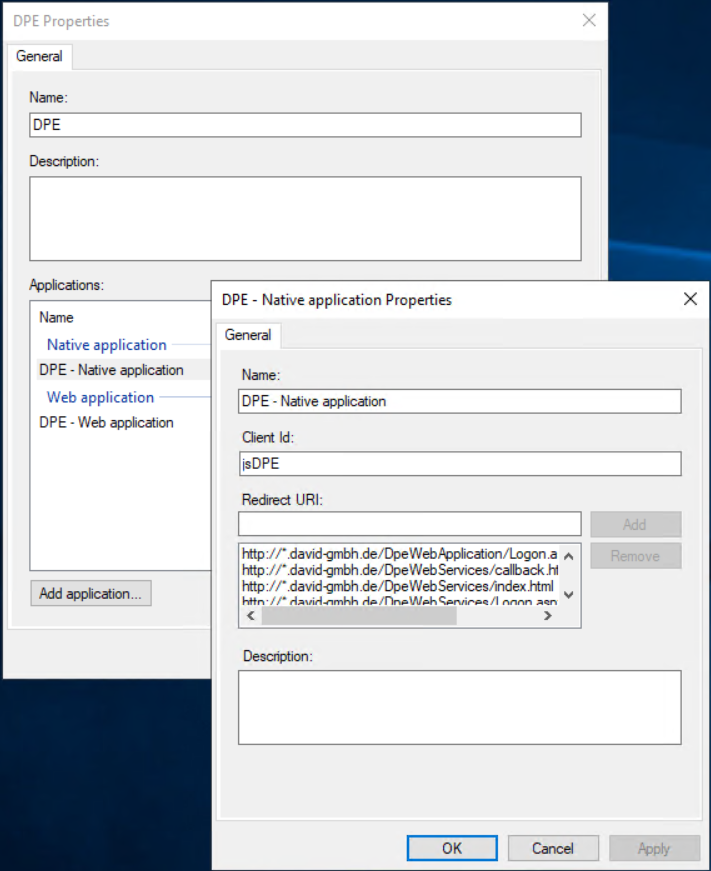
NativeApplications_Properties.png

The DPE web.config would look like...

<add key="AdFsServer" value="https://dpe2019.davidsystems.com/adfs"/>

<add key="ida:AdfsMetadataEndpoint" value="https://dpe2019.davidsystems.com/federationmetadata/2007-06/federationmetadata.xml" />
<add key="ida:Audience" value="microsoft:identityserver:jsDPE" />
<add key="ida:Issuer" value="http://dpe2019.davidsystems.com/adfs/services/trust" />


(3) enable WCF service support for OIDC by adding oidcEndpoint behavior extension and reference it in <behavior name="cors">:

<system.serviceModel>
...
    <behaviors>
      <endpointBehaviors>
        ...
        <behavior name="cors">
          <webHttp/>
          <jsonWebHttp/>
          <enableCorsEndpoint/>
          <oidcEndpoint/>
        </behavior>
      </endpointBehaviors>
    <behaviors>
...
    <extensions>
    ...
      </behaviorExtensions>
        ...
        <add name="oidcEndpoint" type="David.Dpe.Wcf.OidcEndpointBehaviorElement, David.Dpe.Wcf"/>
        ...
      </behaviorExtensions>
    </extensions>   
...
</system.serviceModel>